Jun 2024 - Present Solo lab: build, secure, cost
Cloud Lab
Hands-on infrastructure across AWS, Azure, and GCP: a custom VPC from an empty region up to a reachable web server, then compute, storage, databases, auto scaling, governance, IAM, and a costed game-server design.
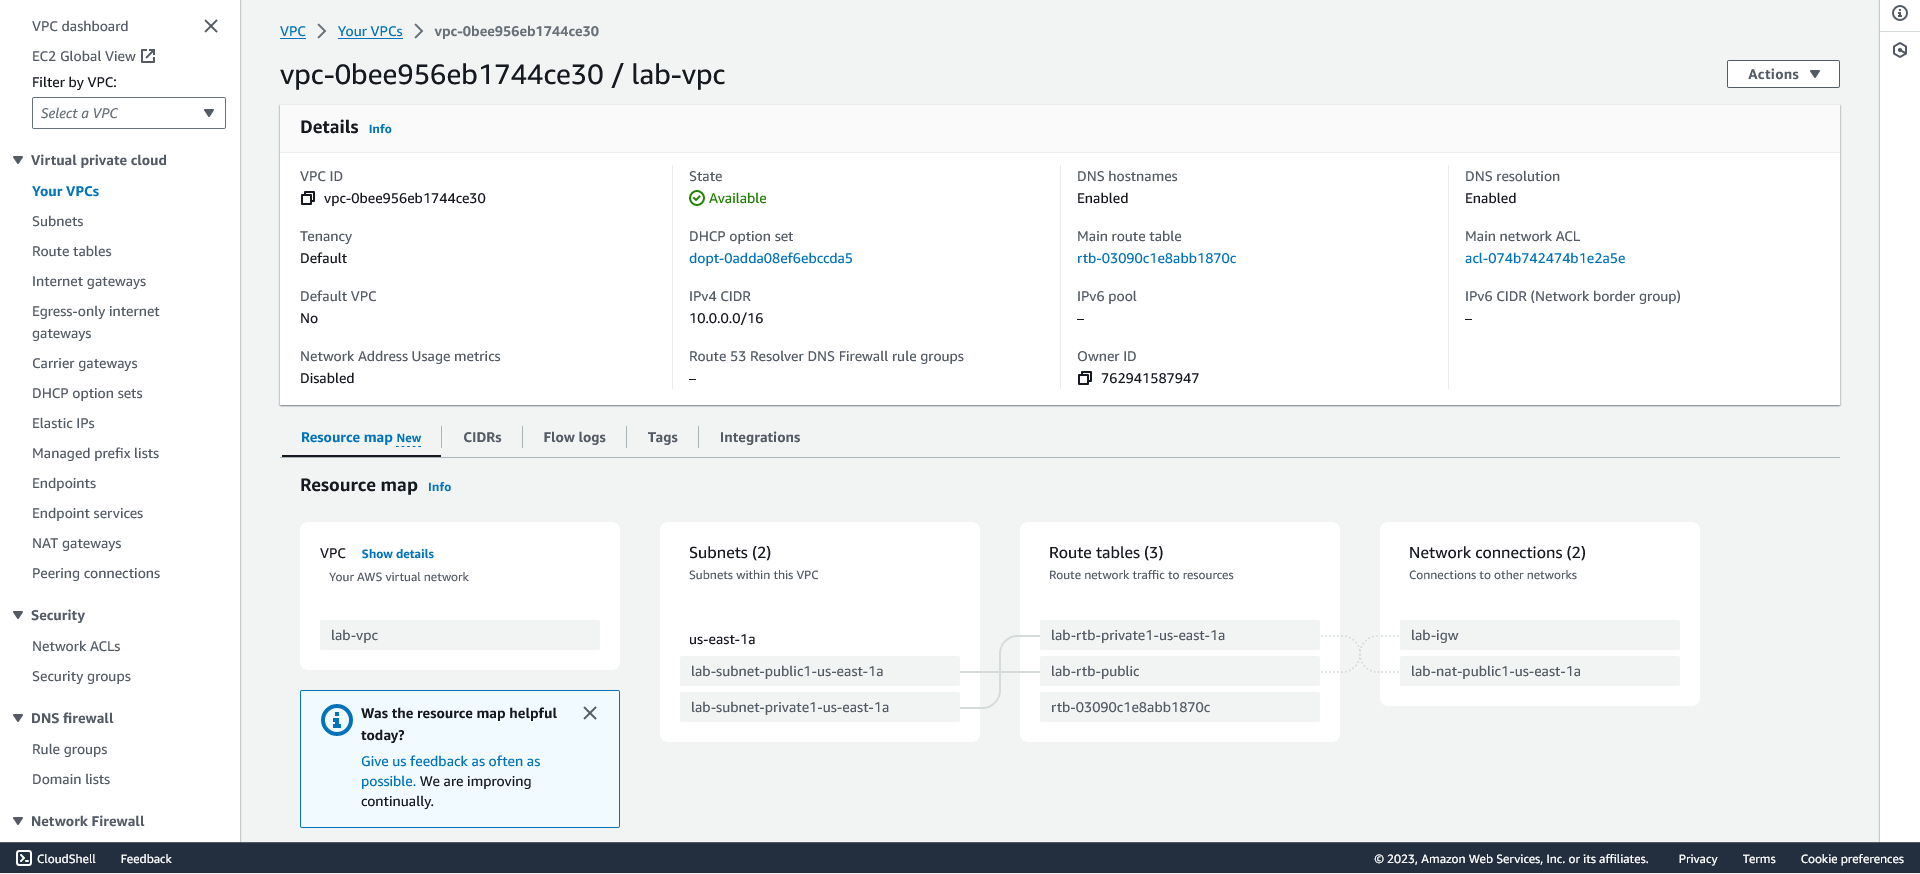
Cloud Lab is hands-on work across the three major cloud providers, written up as the projects I actually built rather than a tour of console features. The weight is on AWS, where I built a custom VPC from an empty region up to an internet-reachable web server, then worked through compute, storage, databases, and auto scaling on top of it. Azure and GCP cover the same fundamentals from each provider angle — resource governance and access control. The last project is my own design proposal for hosting a game server in the cloud, costed out, because deciding what to build is as much the job as clicking it together.
Build it, do not tour it
Cloud Lab is written up as the projects I actually built, not a walk through console wizards. The weight is on AWS: I built a custom VPC from an empty region up to an internet-reachable web server, then layered compute, storage, databases, and auto scaling on top of it.
Azure and GCP cover the same fundamentals from each provider angle — resource governance and access control — and the last project is my own costed design for hosting a game server, because deciding what to build is as much the job as clicking it together.
AWS from an empty region up
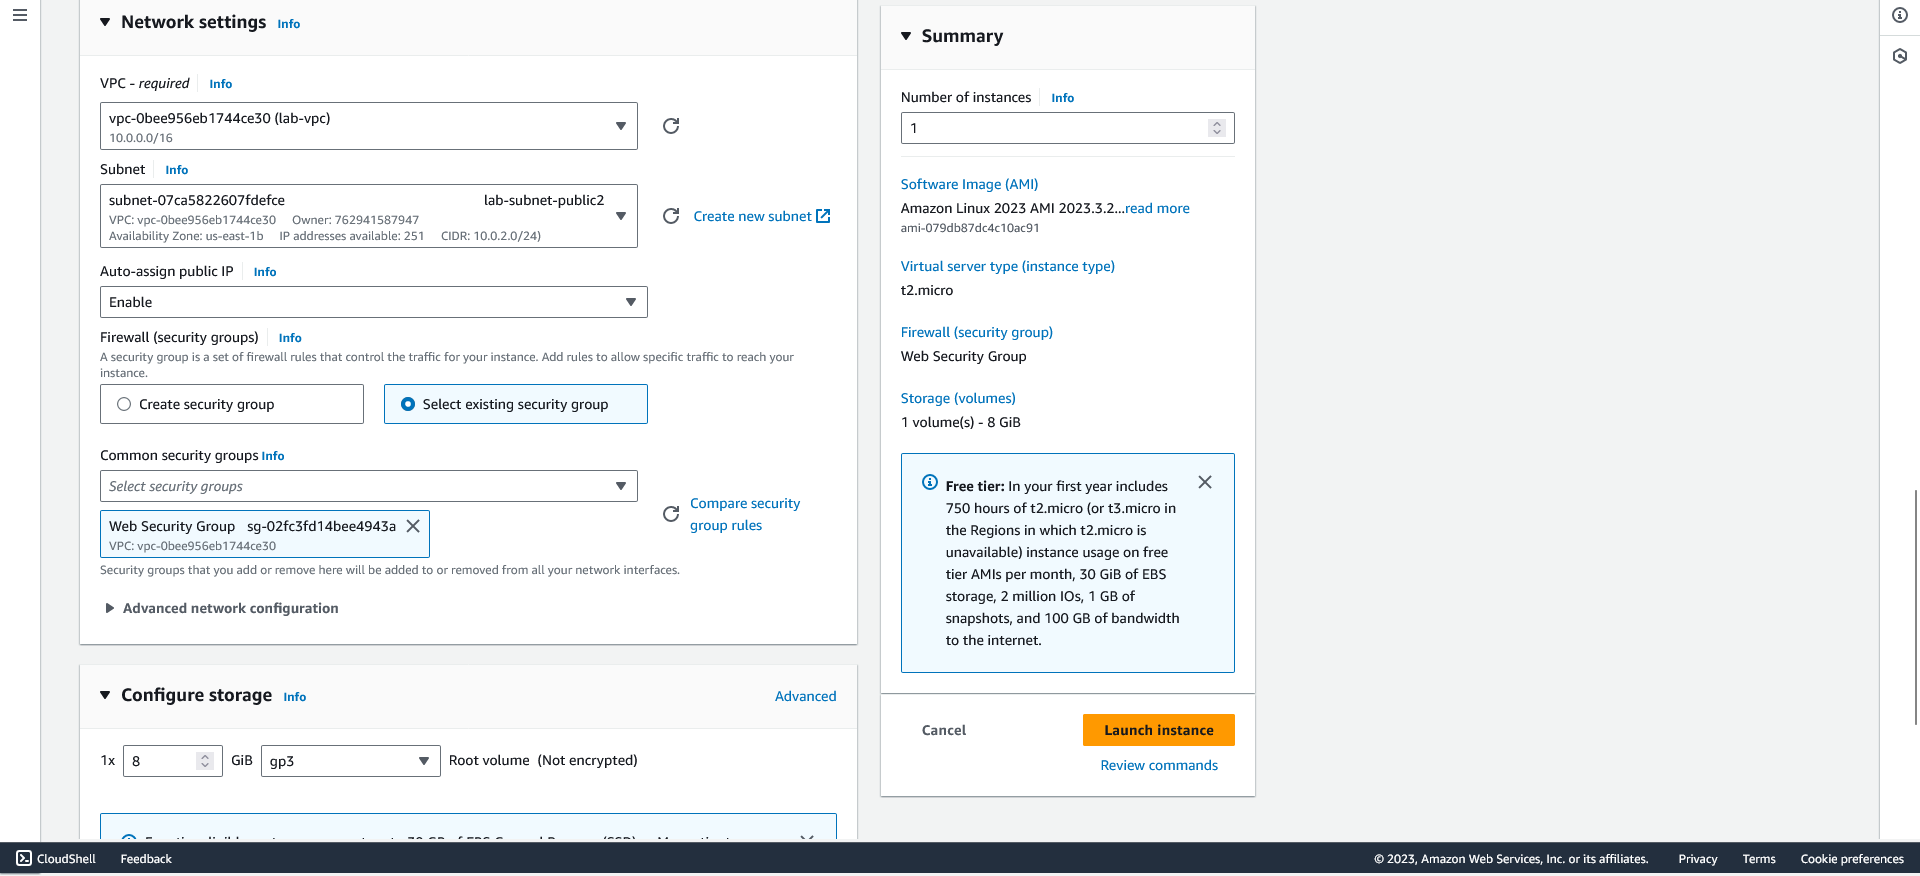
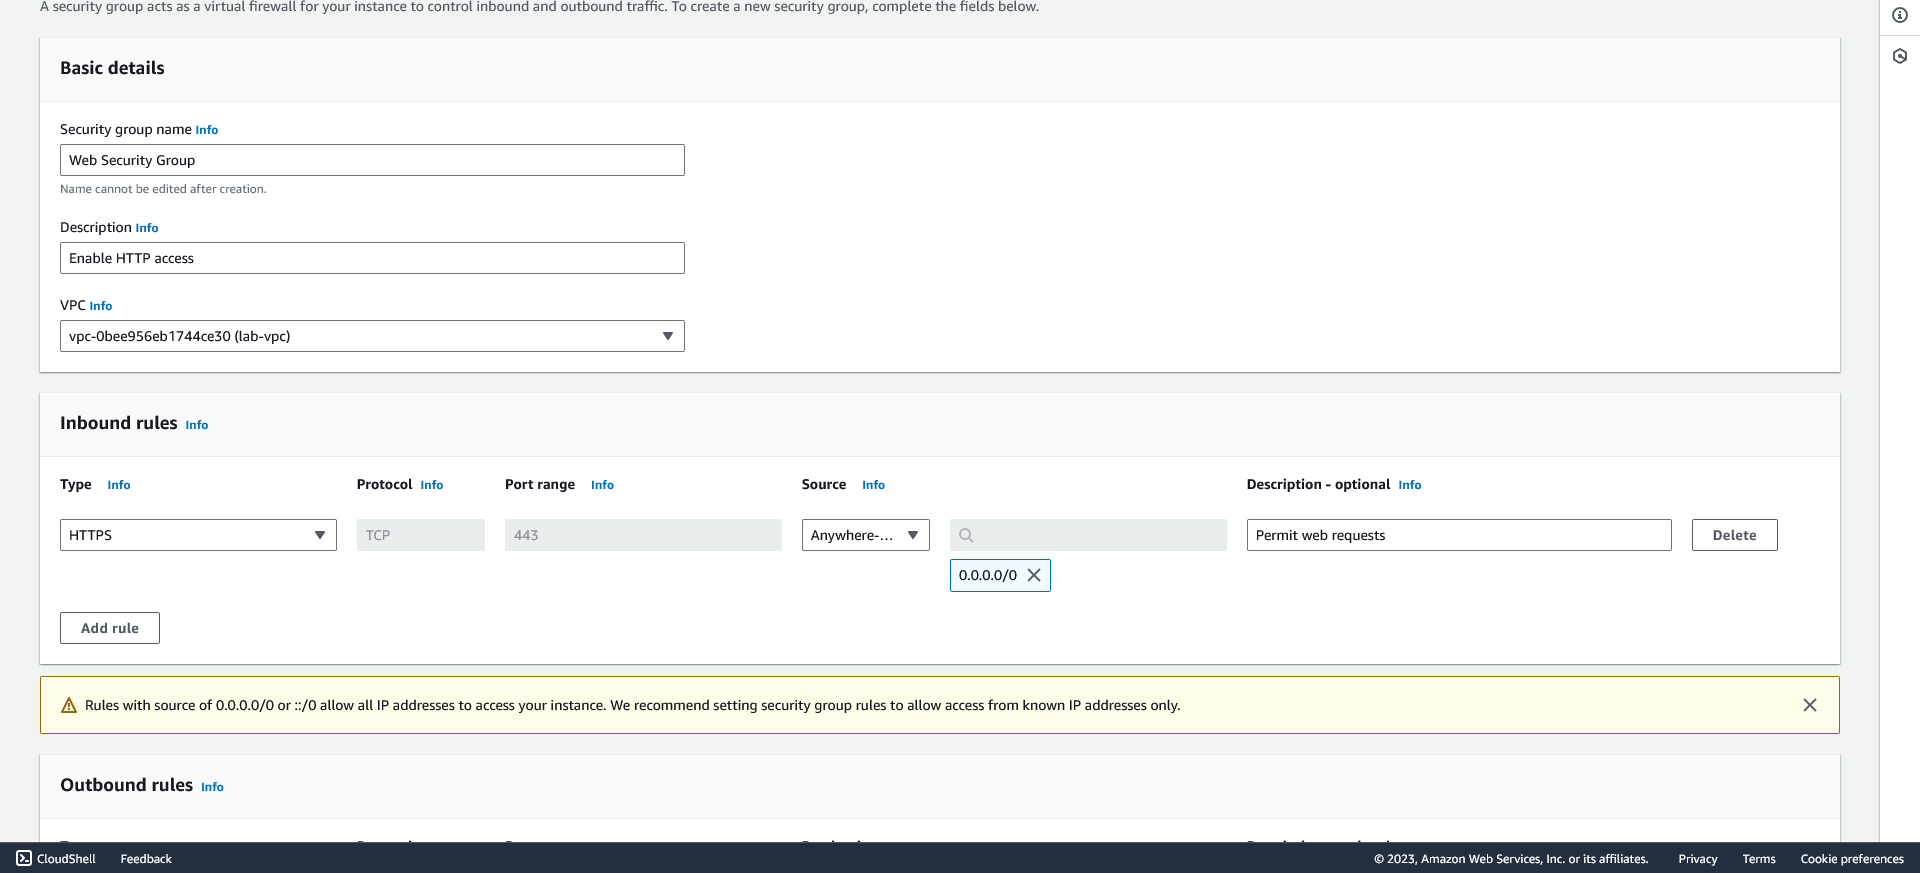
The anchor project builds a VPC with public and private subnets, route tables, an internet gateway, and a security group, then launches an EC2 web server reachable from the internet — end to end, by hand. From there it goes to launching and resizing compute, attaching and snapshotting EBS block storage, and standing up a managed RDS database behind an app.
The scaling project puts a load balancer in front of a self-healing compute pool that grows and shrinks with demand.
Three providers, the same fundamentals
AWS is where the depth is, but the lab covers all three. Azure focuses on resource governance: resource groups, network security rules, storage access levels, and resource locks. GCP focuses on identity: granting and revoking access across accounts, the resource hierarchy, and VM networking from gcloud.
The final project is a design rather than a build — my own architecture and cost estimate for hosting a game server on AWS.
The six projects
Hands-on across all three providers, weighted toward building on AWS:
- 01 · AWS custom VPC & web server
- A VPC, public and private subnets, routing, a security group, and an internet-reachable EC2 web server, end to end
- 02 · AWS EC2, EBS & RDS
- Launching and resizing compute, attaching and snapshotting block storage, and a managed database behind an app
- 03 · AWS scaling & load balancing
- A load-balanced, self-healing compute pool that grows and shrinks with demand
- 04 · Azure resource governance
- Resource groups, network security rules, storage access levels, and resource locks
- 05 · GCP IAM & compute
- Granting and revoking access, the resource hierarchy, and VM networking with gcloud
- 06 · Cloud gaming proposal
- My own design and cost estimate for hosting a game server on AWS